Royal Server Anti-DDoS protection is built for our infrastructure and our clients. We analyze and filter malicious traffic at both network and application level so that services hosted with us remain accessible and stable during security incidents.
> bgp session: established
> l3/l4 filtering: active
> layer7 waf: custom rules loaded
> status: malicious traffic blocked before origin
The Anti-DDoS protection presented on this page is not sold as a separate service. It is part of our infrastructure and is provided exclusively to Royal Server clients for services hosted within our network.
We monitor and filter traffic to reduce the impact of attacks against VPS servers, dedicated servers, colocation services, web platforms and other services operated within the Royal Server infrastructure.
Filtering is adapted to the service and to legitimate traffic patterns. Clients can benefit from custom rules, incident visibility and technical intervention whenever an attack requires additional tuning.
Traffic enters the Royal Server edge, is analyzed in real time, filtered through network and application rules, then delivered to your infrastructure. For each project, we can tune the rules based on the service being run.
UDP floods, SYN floods, scans, request floods and malicious traffic are detected at the edge.
Suspicious packets are blocked while legitimate traffic is preserved for real services.
Websites and APIs are protected with our own rules against bots and exploits.
Delivery via tunnel, cross connect, transit or directly to services hosted at Royal Server.
Clients can benefit from visibility into per-IP filtering, detected attacks and incident details, depending on the protected service.
Each protected IP can have its own filtering rules, tailored for web hosting, VPS, dedicated servers, game servers, business applications or custom infrastructure. We do not apply generic protection; we configure it for the actual traffic.
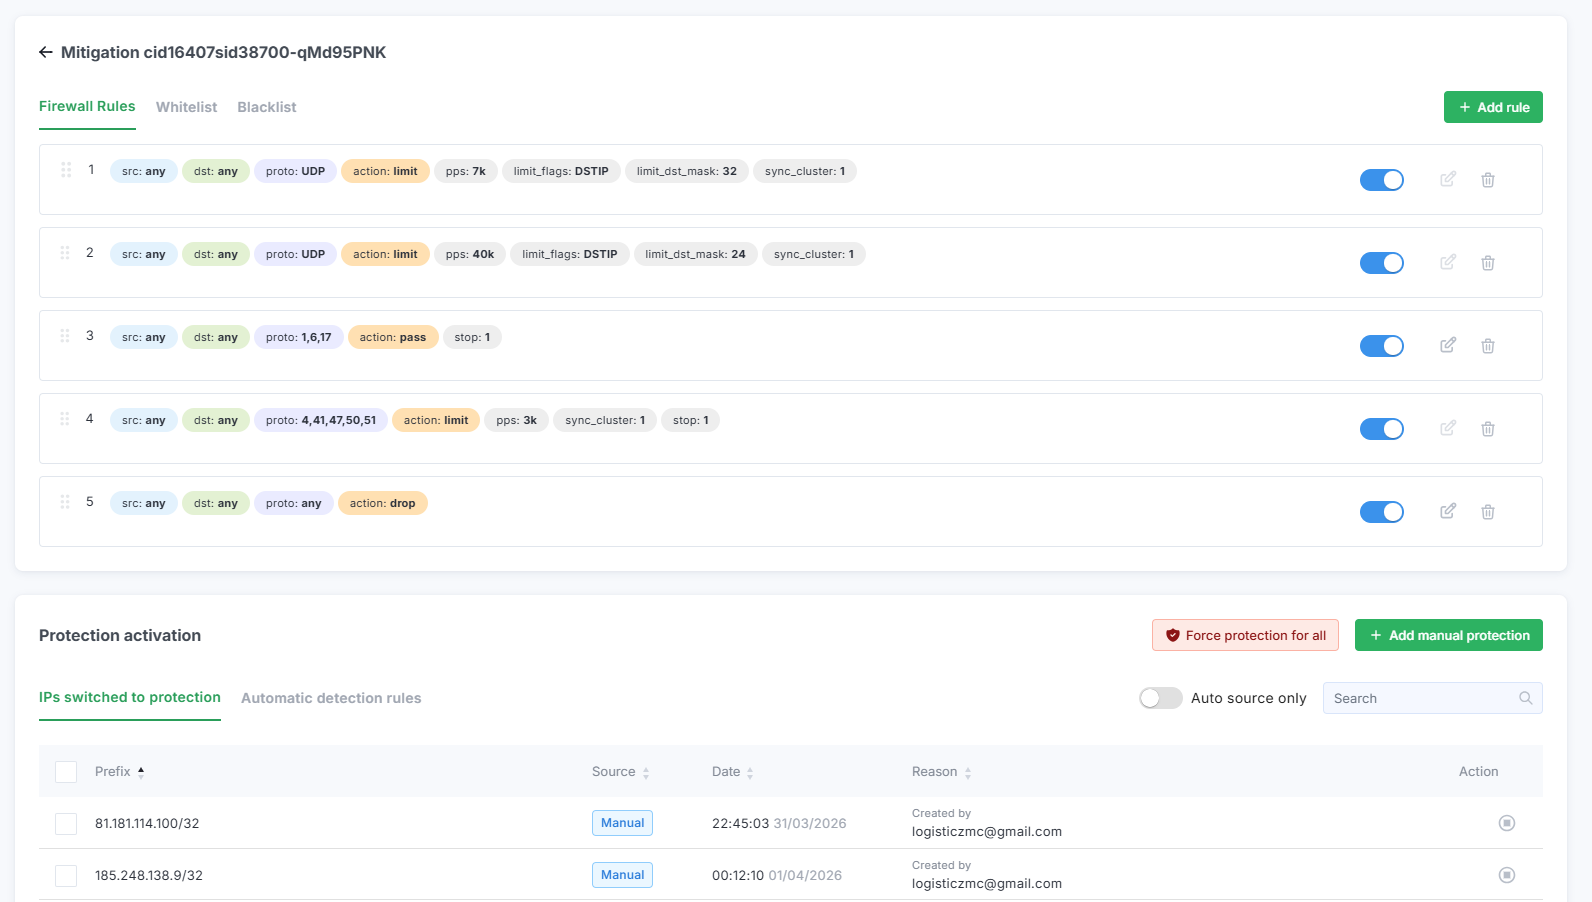
You have a dedicated area where you can view attacks received by your infrastructure. The panel helps identify when an IP is under attack, the type of suspicious traffic and how the protection responds.
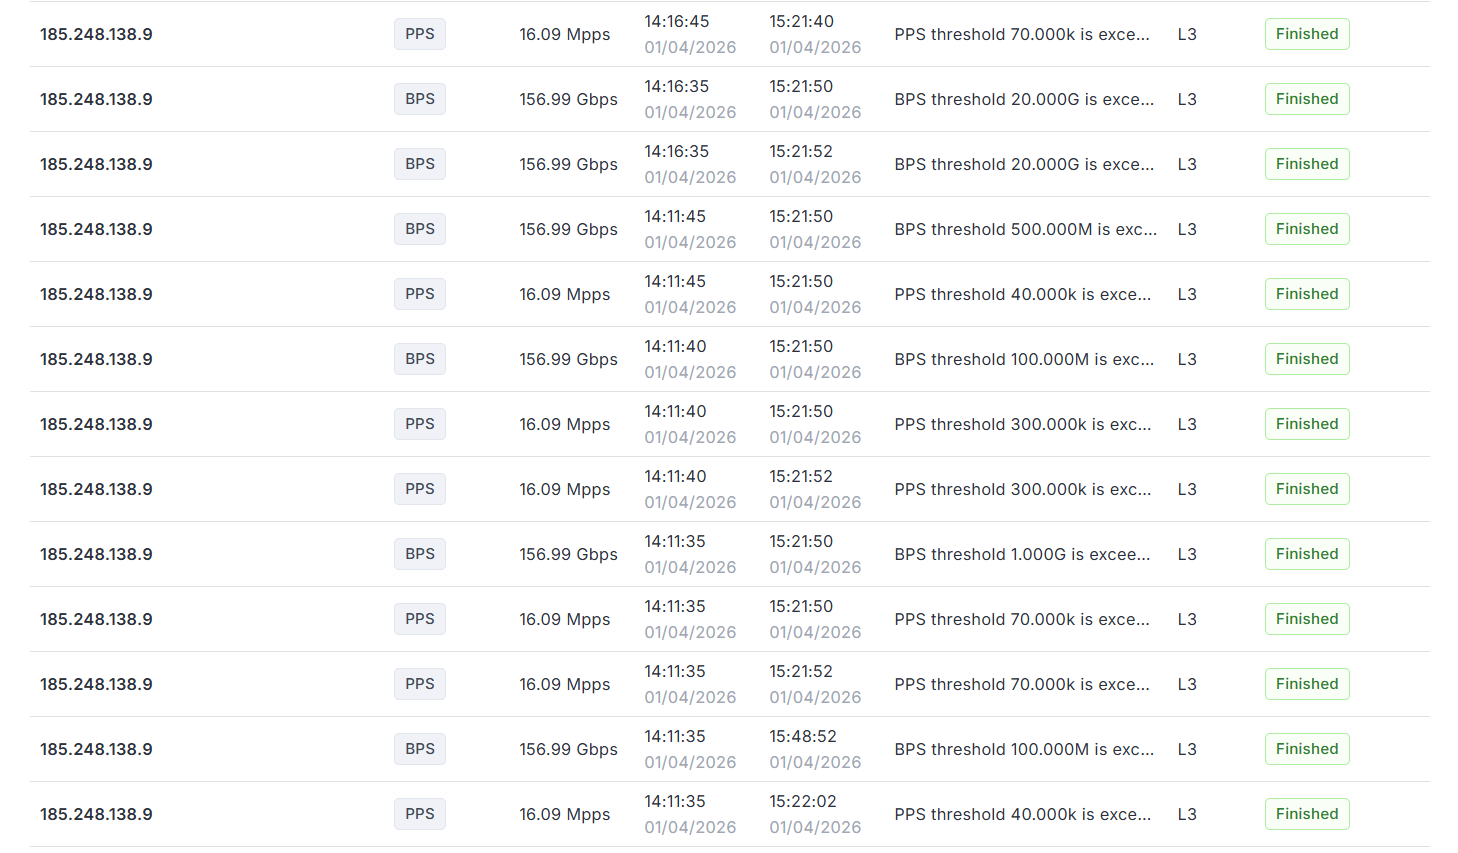
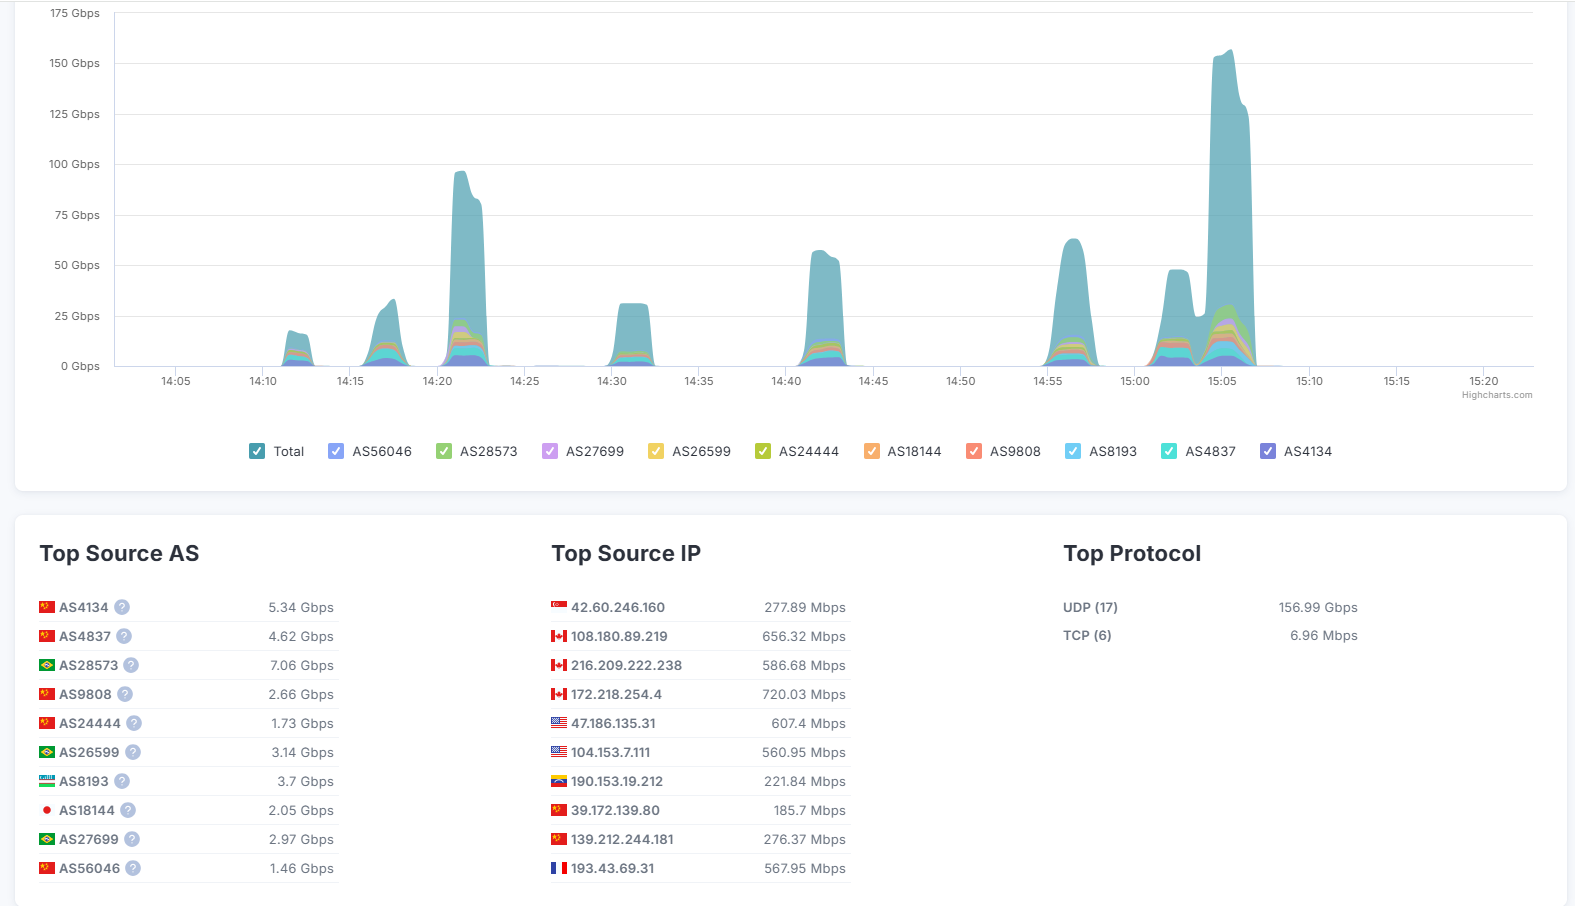
For each attack you can analyze sources, countries, targeted ports, protocols and other useful data. This information helps you understand the vectors used and allows us to tune filters based on real attacks.
In addition to network Anti-DDoS protection, we can use filters on enterprise equipment and Layer 7 rules through our own WAF to reduce malicious traffic before it reaches applications.
These filters are useful against scans, brute force, exploit attempts, bots, request floods, reconnaissance traffic and suspicious traffic targeting ports or web endpoints.
A simple flow for the customer: the attack is received, filtered, and only valid traffic is forwarded.
UDP floods, SYN floods, TCP floods, ICMP floods, request floods, bots and scans are detected automatically.
Network filters and WAF rules block malicious traffic and preserve legitimate traffic.
Your servers receive filtered traffic via tunnel, IP Transit, cross connect or directly within the Royal Server infrastructure.
If one of your services is under attack or requires special filtering rules, open a support ticket. Our team can analyze the incident and tune the protection for your service hosted at Royal Server.
For assistance with protection of services hosted at Royal Server, security incidents or filter adjustments, you can contact us through a support ticket, Telegram or WhatsApp.